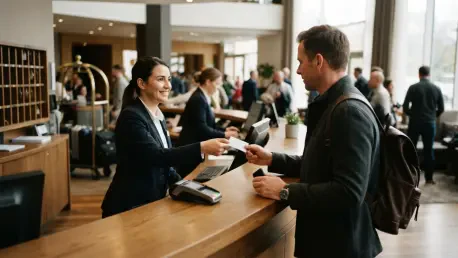
The recurring issue of double-booked rooms and improperly issued key cards reflects a deeper operational vulnerability within the largest hotel chains in the United Kingdom. Travelers who pay for a private room expect that their space is legally and physically secured, yet recent events suggest a significant breakdown in these basic expectations. The hospitality industry operates on a foundation of trust, where the guest assumes the provider has rigorous protocols to prevent unauthorized access. However, when these protocols fail, the result is not just a logistical error but a profound violation of personal privacy. This failure is particularly alarming when it occurs within major organizations that claim to have invested heavily in modern security software and staff training. As the market shifts toward automated check-ins and digital key management, the human and technical errors that allow strangers to enter occupied rooms have become more visible. These incidents raise serious questions about the reliability of systems.
The Glasgow Breach and Security Failures
Analyzing the Incident: Queen Street
The incident involving Jade Clarke at the Queen Street Travelodge in Glasgow serves as a harrowing case study for the dangers of administrative negligence. Clarke, who had booked her room specifically to prepare for a friend’s wedding, was in a state of undress when her door was suddenly opened by two strangers. The couple, who were also paying guests, had been handed a functional key card by the front desk staff that granted them immediate and full access to her private quarters. This moment of exposure was not merely an inconvenience but a significant security breach that left Clarke feeling profoundly vulnerable and unsafe. The immediate shock of seeing strangers in her room while she was unclothed created a sense of violation that no standard apology could easily rectify. While the intruders were reportedly mortified to find the room occupied, the fundamental failure lay with the hotel’s inability to maintain a secure perimeter for a paying guest.
Understanding the Impact: Solo Travelers
The psychological aftermath of such a security lapse extends far beyond the immediate shock, often resulting in long-term anxiety and a total loss of trust in the brand. For solo female travelers, the intrusion colors the entire trip, replacing a sense of safety with a persistent feeling of exposure. Data suggests this is not an isolated event; with unauthorized entries reported at nearly ten percent of locations over a single summer, these lapses represent a systemic issue rather than a series of one-off mistakes. This frequency reveals a widespread vulnerability in operational standards that goes beyond individual staff error. When a guest feels exposed in their most private moments, the emotional toll can manifest as a persistent hyper-vigilance that ruins the purpose of a hotel stay. Travelers now report feeling compelled to use secondary security devices, indicating a crisis of confidence where guests no longer believe provided door locks are sufficient or reliable.
Corporate Responses vs. Guest Safety
Evaluating Official Claims: Rhetoric vs. Reality
Corporate rhetoric often emphasizes rigorous safety improvements, yet high-profile tragedies and recurring errors suggest that these reforms are insufficient. Despite promises made after a sexual assault at a Maidenhead location led to policy changes, the persistence of key card errors proves that the core issue remains unresolved. In that instance, a perpetrator successfully lied to staff to obtain a key, demonstrating a fatal lack of adherence to basic verification protocols. When the company offers apologies or excuses—such as blaming “do not disturb” signs for administrative confusion—it fails to address the fundamental technical and human errors that leave guests at risk. This disconnect suggests a corporate culture that prioritizes operational speed over the absolute security of the guest. Without a fundamental shift in how the organization values privacy, the gap between their public safety promises and the actual conditions in their hotels will continue to grow.
Frequently Asked Questions: Understanding Guest Privacy
- How common are unauthorized room entries at Travelodge? Recent findings indicate that approximately one in ten locations has experienced issues with unauthorized access, suggesting a widespread failure in operational standards. 2. What caused the specific security failure in Glasgow? The breach was caused by a combination of front desk error and a failure in the room allocation software, which allowed a duplicate key card to be issued for an occupied room. 3. How has the hotel chain responded to these safety concerns? While the company issues formal apologies and claims to be leading the industry in security investments, guest experiences suggest a significant gap between these statements and actual room safety. The corporate response typically involves internal investigations and the promise of improved staff training, but these measures have not yet eliminated the occurrence of key card errors. Until high-level technical solutions like two-factor authentication for digital keys are integrated, the promise of safety remains a claim.
Future Security: Actionable Safeguards
The path forward for the hospitality industry requires a total reassessment of how privacy is handled in an increasingly automated environment. To rectify these systemic failures, experts suggest that hotels must implement mandatory secondary verification steps for all key card requests, ensuring that no duplicate can be issued without a confirmed identity check. This transition also involves the adoption of advanced sensor technology that can detect occupancy in real time, feeding that data directly into the front desk software to prevent double-bookings. By moving away from a reliance on manual logs and outdated reservation systems, the industry seeks to close the gaps that allow strangers to enter occupied rooms. These steps are not just about technology; they represent a fundamental shift toward a guest-centric safety model where privacy is treated as a core deliverable. Ultimately, the lessons learned from these incidents force a standard of accountability.